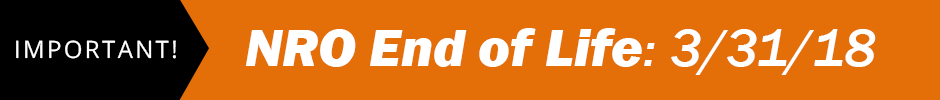
We have been analyzing the NCR Retail Online (NRO) business and our NCR Industry Solutions Board, an internal team that helps set strategy, has decided to set the NRO product to End of Life on March 31, 2018 . The CPOnline Product was also recently announced with an end of life date of September 30th, 2017 . The End of Life terms indicate that all current customers will need to be transitioned off their respective product and the servers turned off by 9/30/17 (CPO) & 3/31/18 (NRO) . Your NCR Counterpoint business partner has been notified of this decision in advance and has started taking steps to help you transition your eCommerce solution.
Next Steps
 As of today, we are encouraging all customers to reach out to your current NCR Counterpoint Partner to begin the transition to a new eCommerce platform. Your partner will be your best resource in planning and transitioning to a new eCommerce solution.
NCR has worked with several partners to create options for your new eCommerce solution. Please refer to the below chart for information about these options. Your partner can provide you with further documentation about these solutions to assist you with the decision process. You can also view a list of FAQ’s about moving from NRO to one of the below options by clicking here .
We will be discussing this transition directly with the users that attend our Synergy User Conference at the end of June. We will be offering a presentation on eCommerce and we will have representatives at the exhibit booth to handle your questions. In the meantime, please reach out to your partner to help determine your next steps.
We appreciate your business and look forward to taking this next, innovative step together.
Recommended eCommerce Solutions
| Solution | Cost | Platform | Additional Notes | |||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| Commerce5 |
|
Magento | Most tightly integrated with Counterpoint and offers the most advanced features | |||||||||||||||||||||
| CP Magento |
|
Magento | Integrated with Counterpoint and offers features similar to NRO | |||||||||||||||||||||
| CP Shop |
|
Woo Commerce | Catalog, Inventory, and Orders are integrated with Counterpoint | |||||||||||||||||||||
Securing Your Move Beyond NCR Retail OnlineThe discontinuation of NCR Retail Online requires merchants to move their ecommerce operations to another platform, often Magento or WooCommerce supported by NCR Counterpoint partners. This transition affects much more than storefront design. Customer accounts, product records, payment connections, staff permissions, integrations, and historical order data all need to be transferred without creating security gaps. A platform migration is a temporary period of elevated risk because information moves between systems, credentials are shared with implementation teams, and old services may remain active longer than expected. Attackers can exploit forgotten administrator accounts, unsecured exports, weak integrations, or domain settings that were changed without proper oversight. A careful plan can preserve customer trust while improving protection. The essential goals are to limit access, safeguard data in transit and at rest, verify the new environment, and retire NCR Retail Online connections cleanly after the replacement store is operating. Map every asset before migrationBegin with a complete inventory of the systems connected to the online store. Include the storefront, Counterpoint or other point-of-sale software, payment gateways, tax services, shipping tools, email marketing accounts, analytics, marketplace feeds, customer support applications, and employee login systems. An unknown connection can become an overlooked route into the new environment. Classify the information held in each system. Customer names, addresses, phone numbers, order histories, login credentials, and loyalty details require different controls from public product descriptions. Payment card data deserves particular care: in many cases, it should remain with a PCI-compliant payment provider rather than being copied into migration files or stored in a general-purpose database. Review the old platform’s exports and backups before downloading them. Use encrypted storage, restrict the people who can access the files, and establish a deletion date. A spreadsheet containing customer records should never sit indefinitely in a shared folder, personal laptop, or unprotected USB drive. Protect accounts and migration credentialsCreate named administrator accounts on the replacement platform instead of relying on one shared login. Assign the smallest practical set of permissions to developers, agency staff, store managers, and support personnel. Someone configuring product imports does not necessarily need access to customer data, payment settings, or server administration. Require multi-factor authentication for the ecommerce dashboard, hosting account, domain registrar, payment provider, email service, and any remote access tools. Strong, unique passwords stored in an approved password manager reduce the risk of credential reuse. Temporary accounts should have an expiration date and should be removed when testing or implementation work ends. API keys, webhooks, private certificates, and application passwords deserve the same attention as user credentials. Keep secrets outside source code and public repositories, rotate them after the migration, and disable credentials belonging to the discontinued system. If an integration must remain active during a transition period, limit its permissions and monitor its use. Validate the new storefront and its integrationsA staging environment provides a safer place to test imports, checkout flows, themes, plugins, and connections with retail management software. Keep staging access-controlled and prevent search engines from indexing it. Test with synthetic customer and order records where possible, especially when third-party developers are involved. Security testing should cover account registration, password resets, administrator pages, checkout, coupon logic, product search, file uploads, and API endpoints. Confirm that a customer cannot view another customer’s order, that staff cannot access functions beyond their role, and that failed login attempts are logged or throttled. The catalog may contain ordinary household goods, yet product content can still expose migration weaknesses if imported carelessly. For example, merchants may review appliance listings for broken images, unsafe HTML, or unexpected scripts before publishing migrated descriptions. Treat all imported fields as untrusted until the new platform sanitizes and validates them.
Secure customer data and privacy controlsData minimization should guide the migration. Move only the records required for ongoing operations and legal obligations. Old guest accounts, unused custom fields, abandoned exports, and duplicate customer profiles increase exposure without necessarily adding business value. Establish retention rules for records that do not need to move. Passwords should never be exported in readable form. If the destination platform cannot accept the source system’s password hashes securely, require customers to create new passwords through a controlled reset process. Communicate that process through verified channels and avoid asking customers to send credentials by email. Review privacy notices, cookie consent settings, marketing permissions, and deletion workflows on the new store. A customer who unsubscribed in the old system should not be added to a new marketing list merely because an import process overlooked the original preference. Test requests for access, correction, and deletion so staff know how to handle them after launch. Harden the storefront after launchBefore changing the live domain, apply security updates to the ecommerce application, extensions, server operating system, and payment components. Magento and WooCommerce environments can be secure, but their risk profile depends heavily on patching, plugin quality, hosting configuration, and administrative discipline. Remove unused extensions and avoid downloading components from unofficial sources. Configure HTTPS across the entire site, redirect legacy HTTP addresses safely, and review DNS records for unexpected entries. Set security headers where compatible with the storefront, protect administrative paths, disable unnecessary server services, and restrict database access. A web application firewall and malware monitoring can provide additional detection, though they should complement secure configuration rather than replace it. Backups need protection from the production environment. Keep encrypted, versioned copies in a separate location, restrict deletion rights, and test restoration before relying on the process. Monitoring should alert the team to unusual administrator logins, payment failures, sudden product changes, repeated password resets, and large data exports. Close the old environment deliberatelyDo not immediately erase NCR Retail Online data or integrations when the new store goes live. First confirm that orders, inventory synchronization, customer service workflows, tax calculations, shipping rules, and reporting operate correctly. Keep a documented rollback window, but make sure the old system is not exposed unnecessarily during that period. When retirement begins, revoke user accounts, API tokens, webhook credentials, remote access permissions, and third-party connections. Remove old DNS records and staging copies, cancel unused services, and ask vendors to confirm the deletion or retention status of stored data. Preserve only the records required for accounting, legal, or support purposes, with appropriate access restrictions. Redirects from old product and category pages should be planned as part of the security and continuity review. For instance, a store migrating dining content can check drinkware pages and everyday dishes for correct destinations, while confirming that redirects cannot be abused to send visitors to unrelated domains. Keep controls active after the moveMigration security is an ongoing operating practice rather than a one-time inspection. Assign an owner for platform updates, access reviews, backup testing, vulnerability response, and vendor communication. Schedule reviews after major plugin changes, payment updates, staff turnover, or new integrations with the Counterpoint environment. Use a short, documented checklist for each release. Verify that staging data is protected, credentials are rotated when needed, logs are retained, and a tested rollback or recovery path exists. Periodic vulnerability scans and an annual independent assessment can identify weaknesses that routine administration misses. Actions that reduce transition risk
A move from NCR Retail Online is an opportunity to replace inherited access and undocumented connections with clearer controls. Start by appointing a migration security owner, involve the NCR Counterpoint partner and payment providers early, and require written evidence for each validation step. Launch the replacement store only after customer data, integrations, accounts, backups, and the retirement of the old environment have all been checked. |
||||||||||||||||||||||||
After you have completed your move to a new eCommerce platform, don’t forget to submit the Store Closure Request form to close your NRO site and cancel your billing subscription.