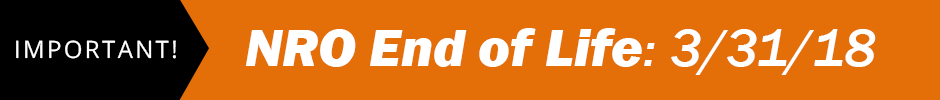
We have been analyzing the NCR Retail Online (NRO) business and our NCR Industry Solutions Board, an internal team that helps set strategy, has decided to set the NRO product to End of Life on March 31, 2018 . The CPOnline Product was also recently announced with an end of life date of September 30th, 2017 . The End of Life terms indicate that all current customers will need to be transitioned off their respective product and the servers turned off by 9/30/17 (CPO) & 3/31/18 (NRO) . Your NCR Counterpoint business partner has been notified of this decision in advance and has started taking steps to help you transition your eCommerce solution.
Next Steps
 As of today, we are encouraging all customers to reach out to your current NCR Counterpoint Partner to begin the transition to a new eCommerce platform. Your partner will be your best resource in planning and transitioning to a new eCommerce solution.
NCR has worked with several partners to create options for your new eCommerce solution. Please refer to the below chart for information about these options. Your partner can provide you with further documentation about these solutions to assist you with the decision process. You can also view a list of FAQ’s about moving from NRO to one of the below options by clicking here .
We will be discussing this transition directly with the users that attend our Synergy User Conference at the end of June. We will be offering a presentation on eCommerce and we will have representatives at the exhibit booth to handle your questions. In the meantime, please reach out to your partner to help determine your next steps.
We appreciate your business and look forward to taking this next, innovative step together.
Recommended eCommerce Solutions
| Solution | Cost | Platform | Additional Notes | ||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| Commerce5 |
|
Magento | Most tightly integrated with Counterpoint and offers the most advanced features | ||||||||||||||||||||||||
| CP Magento |
|
Magento | Integrated with Counterpoint and offers features similar to NRO | ||||||||||||||||||||||||
| CP Shop |
|
Woo Commerce | Catalog, Inventory, and Orders are integrated with Counterpoint | ||||||||||||||||||||||||
Setting up CAPTCHA and fraud rules after leaving NCR Retail OnlineWhen NCR Retail Online was discontinued, hundreds of Australian merchants suddenly had to rebuild security layers they had previously taken for granted. For many Sydney and Melbourne shops running through Counterpoint partners, the migration to Magento or WooCommerce opened up fresh customisation, but it also exposed gaps in automated bot defence and checkout fraud screening. The good news is that the same safeguards NCR once bundled into the platform can be recreated with the right combination of plugins, scripts, and platform rules. Captcha and fraud-rule configuration sit at the intersection of customer experience and risk management. A store that over-engineers its challenges risks losing Brisbane shoppers mid-checkout, while a store that does too little ends up absorbing chargebacks from card-testing bots that probe Australian BIN ranges at all hours. The sections below walk through how Australian retailers can layer protections onto a new storefront without leaning on legacy NCR tooling, and how to keep those layers tuned as conditions change through the year. Why CAPTCHA still matters in the post-NCR landscapeAutomated traffic now accounts for a substantial share of retail ecommerce requests, and Australian storefronts are not exempt. Bots attempt to scrape pricing from Adelaide-based competitors, brute-force coupon codes against Perth stores, and stockpile limited-release products ahead of Click Frenzy events. A visible challenge at the right moment — on signup, at checkout, or after a spike of failed attempts — stops the majority of these probes without troubling genuine shoppers. Beyond raw bot blocking, challenge systems also act as a deterrent. Once attackers recognise that an endpoint is hardened, they typically move on to softer targets. For a small business operating in Hobart or Darwin with limited dev resources, even a basic challenge layer buys meaningful protection while the team focuses on merchandising. The challenge is choosing an implementation that does not slow the page down, does not break accessibility, and does not lock out assistive technology users, which is a stated requirement under the Disability Discrimination Act. Building bot defences without native toolsWithout a built-in security module, the replacement stack needs explicit configuration. The most common path for Magento merchants is to install a maintained CAPTCHA extension and pair it with rate-limiting at the web server or CDN edge. WooCommerce shop owners typically rely on plugins such as reCAPTCHA for WooCommerce or honeypot fields that silently trap non-human submissions. Both approaches can be deployed without touching custom code, which matters when the migration team is already stretched. The shift away from NCR's integrated dashboards also means logs live in different places. Order anomalies show up in the platform backend, bot traffic appears in the CDN analytics, and challenge failures sit in the CAPTCHA provider console. Consolidating these signals into a single weekly review is a habit that pays off quickly, particularly in the lead-up to seasonal peaks. Retailers preparing for seasonal promotions often find that the previous year's bot patterns repeat with only minor variations, and a documented baseline makes it easier to spot fresh waves. Crafting fraud rules for Australian conditionsDefault fraud screens in most ecommerce platforms were designed with the US market in mind. They often flag orders shipping to Australian states that the original training data treated as unusual, and they routinely decline legitimate postcodes around regional Queensland or Western Australia. Writing local rules — rather than relying on out-of-the-box thresholds — closes that gap. A practical starting point is to define velocity rules based on the realities of Australian shipping. An order with three different cards shipping to the same Sydney address within ten minutes is almost always fraud, while a single card with two separate deliveries to a Canberra home and a click-and-collect pickup in Woden is probably a busy parent. Layer in AVS checks for cardholder address, postcode validation against the Australia Post database, and a manual review queue for orders above a sensible threshold such as AUD 500. These rules can be tuned per category, since high-value electronics in Melbourne attract different risk patterns than a thirty-dollar accessory shipped from a Brisbane warehouse. For merchants moving from a managed environment, a useful reference is redundant inventory checks, since the same parallel-validation mindset applies to fraud signals. Treating every rule as a checkpoint rather than a gate keeps legitimate orders flowing while suspicious ones get a second look. Configuring rules in your replacement platformMagento gives merchants the most granular control through its built-in payment and shipping rules, combined with extensions for advanced risk scoring. WooCommerce leans on a wider plugin ecosystem, with services like Anti-Fraud, Signifyd, and Kount covering different price points. In both cases, the configuration workflow follows a similar pattern: define triggers, decide on actions, test against historical orders, then monitor live performance. Testing is the step that gets skipped most often. Before flipping rules on for real traffic, replay six months of recorded orders through the new configuration and compare outcomes against actual chargeback and dispute data. This is also the moment to verify that local payment methods — including Australia Post eParcel shipping calculations and PayPal Australia flows — still complete cleanly. A configuration that triggers on a PayPal billing address mismatch in Adelaide will create support tickets faster than it stops fraud. Documentation matters as much as the rules themselves. Store owners who recently transitioned often describe what retailers miss most, and centralised reporting usually tops that list. Building a lightweight dashboard in the new stack — even a weekly CSV export emailed to the operations lead in Brisbane — replicates that visibility without the original platform. Monitoring and tuning over timeFraud patterns shift faster than most retailers update their documentation. A rule that blocked 90 percent of card-testing attempts in March may become irrelevant by July, replaced by a new botnet that uses residential Australian IP ranges. Continuous monitoring, even at a basic level, is what keeps defences aligned with the threat. Set a monthly review window, compare dispute rates from the payment gateway against the previous period, and look for unexplained spikes in declined checkouts. Use the Scamwatch and Australian Cyber Security Centre advisories as a free early-warning feed, since they publish emerging patterns that often show up in retail fraud data within weeks. Finally, revisit challenge difficulty seasonally: a lighter CAPTCHA during a Boxing Day sale reduces cart abandonment, while a stricter version after the rush catches the cleanup wave that follows.
Common triggers worth configuring first
Signals that a rule needs attention
The single most useful habit is treating fraud configuration as a living system rather than a launch checklist. A store in Parramatta or Geelong that reviews its rules every quarter will quietly outperform one that set everything up once and never touched it again, because the threat environment never sits still and the local patterns — from Click Frenzy traffic surges to post-Christmas return waves — keep reshaping what "normal" looks like. |
|||||||||||||||||||||||||||
After you have completed your move to a new eCommerce platform, don’t forget to submit the Store Closure Request form to close your NRO site and cancel your billing subscription.