We have been analyzing the NCR Retail Online (NRO) business and our NCR Industry Solutions Board, an internal team that helps set strategy, has decided to set the NRO product to End of Life on March 31, 2018 . The CPOnline Product was also recently announced with an end of life date of September 30th, 2017 . The End of Life terms indicate that all current customers will need to be transitioned off their respective product and the servers turned off by 9/30/17 (CPO) & 3/31/18 (NRO) . Your NCR Counterpoint business partner has been notified of this decision in advance and has started taking steps to help you transition your eCommerce solution.
Next Steps
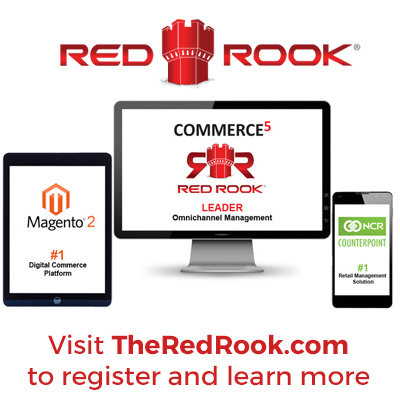 As of today, we are encouraging all customers to reach out to your current NCR Counterpoint Partner to begin the transition to a new eCommerce platform. Your partner will be your best resource in planning and transitioning to a new eCommerce solution.
NCR has worked with several partners to create options for your new eCommerce solution. Please refer to the below chart for information about these options. Your partner can provide you with further documentation about these solutions to assist you with the decision process. You can also view a list of FAQ’s about moving from NRO to one of the below options by clicking here .
We will be discussing this transition directly with the users that attend our Synergy User Conference at the end of June. We will be offering a presentation on eCommerce and we will have representatives at the exhibit booth to handle your questions. In the meantime, please reach out to your partner to help determine your next steps.
We appreciate your business and look forward to taking this next, innovative step together.
Recommended eCommerce Solutions
| Solution | Cost | Platform | Additional Notes |
|---|---|---|---|
| Commerce5 |
|
Magento | Most tightly integrated with Counterpoint and offers the most advanced features |
| CP Magento |
|
Magento | Integrated with Counterpoint and offers features similar to NRO |
| CP Shop |
|
Woo Commerce | Catalog, Inventory, and Orders are integrated with Counterpoint |
Hardening your new stack after a platform migrationWhen retailers move from a legacy system to a modern ecommerce engine like Magento or WooCommerce, the excitement of a fresh interface can distract from the unglamorous work that follows. A new stack introduces new code paths, new admin accounts, and new points where customer data can leak. A deliberate security sweep in the weeks after cutover protects revenue, reputation, and the trust of shoppers who have no reason to care about your backend. Australian merchants in particular operate under the Australian Privacy Principles and the Notifiable Data Breaches scheme, so a quiet lapse can turn into an OAIC reportable incident faster than many owners expect. Whether you are running a boutique in Fitzroy or a multi-store operation spanning Sydney, Brisbane, and Perth, the post-migration window is when small oversights quietly compound into recurring problems that erode margins and customer confidence over time. Why a post-migration security review cannot waitMost migration projects focus on getting product data flowing and orders placing cleanly, and security testing often gets squeezed into the last weekend before launch. Once the site is live and revenue is coming through, the temptation is to leave the configuration alone and focus on growth campaigns. That instinct is understandable but risky. The new platform has different default settings, different admin URLs, and different extension behaviour than the system you left behind, and any of those differences can quietly expose information that was previously hidden. A structured review also gives you a baseline. Once you know what is hardened and what is exposed, you can detect drift later when an extension update or a contractor change introduces a regression. Without that snapshot, you are essentially flying blind and hoping that nothing changes behind the scenes. The baseline also makes audits easier when a partner, insurer, or regulator asks what controls you have in place. Foundational checks before going deeperBefore diving into complex penetration testing, walk through the basics that catch most oversights. These are the items that are easy to miss during a rushed cutover and inexpensive to fix once flagged, yet they remain the source of the majority of post-launch incidents. Core verification items
These checkpoints sound obvious, yet cutover pressure in a Brisbane or Perth office often means one of them gets skipped in the rush to process the first real orders. A second set of eyes during the first week catches what the launch team missed. Spotting data leaks and inventory gapsOnce the foundations look clean, turn attention to the data layer where most silent failures originate. Migrations that use flat-file imports can drop characters, truncate fields, or duplicate rows in ways that do not show up until weeks later when a customer complains about a missing order or a duplicated charge. A reconciliation pass against trusted pre-migration numbers is the only reliable way to confirm parity across products, customers, and order history. The pre-migration inventory reports walk through the specific exports that catch most discrepancies, and running them again post-launch helps confirm nothing drifted during the freeze window. Look for orphaned customer records, orders stuck in pending states, and pricing that does not match the GST-inclusive totals your finance team expects. Australian shoppers are quick to spot a price that excludes the 10 percent goods and services tax when it should not, and those support tickets are an early warning that something in the data pipeline is misbehaving. Audit logs from the migration window often reveal whether the issue originated in the source system or in the import script. Payment gateways and access controlsPayment configuration deserves its own audit pass because the financial blast radius of a mistake is much larger than a leaked product image. Confirm that your gateway supports the methods Australian customers actually use, including POLi for direct bank transfers, BPAY for bill-style payments, and Afterpay for buy-now-pay-later shoppers who expect it on most non-food retail sites. The process of connecting payment gateways deserves fresh attention, particularly if your old system handled tokenisation in a way the new platform does not replicate, since stored cards from the old vault often need to be re-tokenised through the new integration. Confirm refund and chargeback flows end-to-end before relying on them in a live dispute. Review who has admin access, who has read-only access to customer PII, and whether any former staff or contractor accounts were carried across from the legacy environment. AEST or AEDT timestamps in your audit logs make incident reconstruction far easier when you are chasing an event at 2am during daylight saving crossover, so make sure the logging library is configured for Australia rather than the default UTC. Aligning log time with local wall-clock time also helps when correlating with customer support tickets, which arrive in local time. Documentation and monitoring going forwardA migration is a snapshot, but security is a moving target. The habits you establish in the first month determine whether the new stack stays hardened or quietly relaxes back into bad defaults as plugins are added and staff change. Keeping clear workflow documentation means the next person to touch the site does not have to reverse-engineer decisions made during the cutover, and it gives your accountant or compliance officer a paper trail when they ask why a particular control is in place. Recurring hygiene tasksBuild a small, repeatable hygiene routine into your operations calendar so it does not depend on memory or goodwill:
The Australian ecommerce market keeps rewarding merchants who treat post-launch as the real start of platform ownership rather than the finish line. A focused security audit in the weeks after migration pays for itself the first time it catches a misconfigured webhook or a stale API key before either becomes a customer-facing problem. Treat the audit as a recurring habit rather than a one-off project, and your new stack will repay the attention with fewer incidents, calmer support queues, and steadier growth across the quarters that matter. |
|||
After you have completed your move to a new eCommerce platform, don’t forget to submit the Store Closure Request form to close your NRO site and cancel your billing subscription.